Hani Samimi

An information security management system (ISMS) is, as the name implies, a set of policies concerned with information security management. The idiom arose primarily out of ISO/IEC 27001.
The governing principle behind an ISMS is that an organization should design, implement and maintain a coherent set of processes and systems to manage risks to its information assets, thus ensuring acceptable levels of information security (usually summarised as confidentiality, integrity and availability).
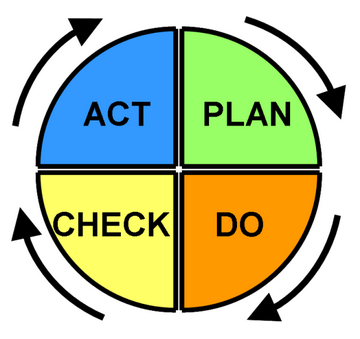
As with all management processes, an ISMS must remain effective and efficient in the long term, adapting to changes in the internal organization and external environment. ISO/IEC 27001 therefore incorporates the typical "Plan-Do-Check-Act" (PDCA), or Deming cycle, approach:
  1. The Plan phase is about designing the ISMS, assessing information security risks and selecting appropriate controls.
  2. The Do phase involves implementing and operating the controls.
  3. The Check phase objective is to review and evaluate the performance (efficiency and effectiveness) of the ISMS.
  4. In the Act phase, changes are made where necessary to bring the ISMS back to peak performance.
The best known ISMS is described in ISO/IEC 27001 and ISO/IEC 27002 and related standards published jointly by ISO and IEC.
Another competing ISMS is Information Security Forum's Standard of Good Practice (SOGP). It is more best practice-based as it comes from ISF's industry experiences.
Other frameworks such as COBIT and ITIL touch on security issues, but are mainly geared toward creating a governance framework for information and IT more generally.
Hani Samimi

Information security means protecting information and information systems from unauthorized access, use, disclosure, disruption, modification or destruction.
The terms information security, computer security and information assurance are frequently incorrectly used interchangeably. These fields are interrelated often and share the common goals of protecting the confidentiality, integrity and availability of information; however, there are some subtle differences between them.
These differences lie primarily in the approach to the subject, the methodologies used, and the areas of concentration. Information security is concerned with the confidentiality, integrity and availability of data regardless of the form the data may take: electronic, print, or other forms.
Computer security can focus on ensuring the availability and correct operation of a computer system without concern for the information stored or processed by the computer.
Governments, military, corporations, financial institutions, hospitals, and private businesses amass a great deal of confidential information about their employees, customers, products, research, and financial status. Most of this information is now collected, processed and stored on electronic computers and transmitted across networks to other computers.
Should confidential information about a business' customers or finances or new product line fall into the hands of a competitor, such a breach of security could lead to lost business, law suits or even bankruptcy of the business. Protecting confidential information is a business requirement, and in many cases also an ethical and legal requirement.
For the individual, information security has a significant effect on privacy, which is viewed very differently in different cultures.
The field of information security has grown and evolved significantly in recent years. As a career choice there are many ways of gaining entry into the field. It offers many areas for specialization including: securing network(s) and allied infrastructure, securing applications and databases, security testing, information systems auditing, business continuity planning and digital forensics science, to name a few, which are carried out by Information Security Consultants